Wednesday, June 10, 2020

Ask And You Shall Receive


I get emails from readers asking for specific malware samples and thought I would make a mini post about it.

Yes, I often obtain samples from various sources for my own research.

 I am sometimes too lazy/busy to post them but don't mind sharing.
If you are looking for a particular sample, feel free to ask. I might have it.

Send MD5 (several or few samples). I cannot provide hundreds/thousands of samples or any kind of feeds. If you ask for a particular family, I might be able to help if I already have it.

Unfortunately, I do not have time to do homework for students and provide very specific sets for malware with specific features as well as guarantee the C2s are still active.  Send your MD5(s) or at least malware family and I check if I have it :) If i have it, I will either send you or will post on the blog where you can download.

If you emailed me in the past and never got an answer, please remind me. Sometimes emails are long with many questions and I flag them to reply to later, when I have time and they get buried or I forget. It does not happen very often but accept my apologies if it happened to you.

Before you ask, check if it is already available via Contagio or Contagio Mobile.
1. Search the blog using the search box on the right side
2. Search here https://www.mediafire.com/folder/b8xxm22zrrqm4/BADINFECT
3. Search here https://www.mediafire.com/folder/c2az029ch6cke/TRAFFIC_PATTERNS_COLLECTION
4. Search here https://www.mediafire.com/folder/78npy8h7h0g9y/MOBILEMALWARE

Cheers,  Mila

More articles


Tuesday, June 9, 2020

Microsoft Releases June 2020 Security Patches For 129 Vulnerabilities

Microsoft today released its June 2020 batch of software security updates that patches a total of 129 newly discovered vulnerabilities affecting various versions of Windows operating systems and related products. This is the third Patch Tuesday update since the beginning of the global Covid-19 outbreak, putting some extra pressure on security teams struggling to keep up with patch management

via The Hacker News

Related articles


  1. Pentest Os
  2. Hacking Tools
  3. Hacking Apps
  4. Pentestgeek
  5. Pentest Magazine
  6. Hacking Typer
  7. Hacking Programs
  8. Pentest Software
  9. Pentest Gear
  10. Hacking Online Games
  11. Hacking Wifi
  12. Pentest Nmap
  13. Pentest Kit
  14. Pentest Standard
  15. Hacking Jailbreak
  16. Pentest Vs Ceh
  17. Pentest Stages
  18. Pentest Iso
  19. Pentest Wiki
  20. Pentest Firewall

Vsftpd Backdoor - Ekoparty Prectf - Amn3S1A Team

It's a 32bits elf binary of some version of vsftpd, where it have been added a backdoor, they don't specify is an authentication backdoor, a special command or other stuff.

I started looking for something weird on the authentication routines, but I didn't found anything significant in a brief period of time, so I decided to do a bindiff, that was the key for locating the backdoor quickly. I do a quick diff of the strings with the command "strings bin | sort -u" and "vimdiff" and noticed that the backdoored binary has the symbol "execl" which is weird because is a call for executing elfs, don't needed for a ftp service, and weird that the compiled binary doesn't has that symbol.


Looking the xrefs of "execl" on IDA I found that code that is a clear backdoor, it create a socket, bind a port and duplicate the stdin, stdout and stderr to the socket and use the execl:


There are one xrefs to this function, the function that decides when trigger that is that kind of systems equations decision:


The backdoor was not on the authentication, it was a special command to trigger the backdoor, which is obfuscated on that systems equation, it was no needed to use a z3 equation solver because is a simple one and I did it by hand.


The equation:
cmd[0] = 69
cmd[1] = 78
cmd[1] + cmd[2] = 154
cmd[2] + cmd[3] = 202
cmd[3] + cmd[4] = 241
cmd[4] + cmd[5] = 233
cmd[5] + cmd[6] = 217
cmd[6] + cmd[7] = 218
cmd[7] + cmd[8] = 228
cmd[8] + cmd[9] = 212
cmd[9] + cmd[10] = 195
cmd[10] + cmd[11] = 195
cmd[11] + cmd[12] = 201
cmd[12] + cmd[13] = 207
cmd[13] + cmd[14] = 203
cmd[14] + cmd[15] = 215
cmd[15] + cmd[16] = 235
cmd[16] + cmd[17] = 242

The solution:
cmd[0] = 69
cmd[1] = 75
cmd[2] = 79
cmd[3] = 123
cmd[4] = 118
cmd[5] = 115
cmd[6] = 102
cmd[7] = 116
cmd[8] = 112
cmd[9] = 100
cmd[10] = 95
cmd[11] = 100
cmd[12] = 101
cmd[13] = 106
cmd[14] = 97                    
cmd[15] = 118
cmd[16] = 117
cmd[17] = 125


The flag:
EKO{vsftpd_dejavu}

The binary:
https://ctf.ekoparty.org/static/pre-ekoparty/backdoor


Related news


Tricks To Bypass Device Control Protection Solutions

Preface

As I wrote in a previous blog post, I had an engagement last year where my task was to exfiltrate data from a workstation on some sort of storage media. The twist in that task was Lumension Sanctuary Device Control, and the version was 4.3.2, but I am not sure how newer version work and this seems to be a more general problem with device control solution, for example with Symantec products.

But what is a device control solution? In short, they audit I/O device use and block the attempts to use unauthorized devices. This includes hardware such as USB, PS/2, FireWire, CD/DVD so basically every I/O port of a computer. In my opinion, these are pretty good things and they offer a better looking solution than de-soldering the I/O ports from the motherboards or hot-gluing them, but on the other hand, they can be bypassed.

Bypass

OK, so what is the problem? Well the way these device control solutions work is that they load a few kernel drivers to monitor the physical ports of the machine. However... when you boot up the protected computer in safe mode, depending on the device control solution software, some of these drivers are not loaded (or if you are lucky, none of those modules will be loaded...) and this opens up the possibility to exfiltrate data.

In theory, if you have admin (SYSTEM maybe?) privileges, you might as well try to unload the kernel drivers. Just do not forget, that these device control solutions also have a watchdog process, that checks the driver and automatically loads it back if it is unloaded, so look for that process and stop or suspend it first.

In my case with the Lumension Sanctuary Device Control, I have found that when I boot the Workstation protected by the device control software in Safe Mode where, software's key logger protection module is not running... so I was still unable to use a USB stick, or a storage media, but I could plug in a keyboard for example...hmmm :)

As some of you probably already figured it out, now it is possible to use a pre-programmed USB HID, for example a Teensy! : ) I know about three different project, that uses this trick like these two mentioned in a Hackaday post, or this one. Unfortunately, the site ob-security.info no longer seems to be available (well, at least it is no longer related to infosec :D ), but you can still find the blog post and the files with the Wayback Machine.

For the hardware part, the wiring of the Teensy and the SD card adaptor is the same as I showed in the post on Making a USB flash drive HW Trojan or in the Binary deployment with VBScript, PowerShell or .Net csc.exe compiler post, so I will not copy it here again.

I have to note here that there are other ways to bypass these device control solutions, like the method what Dr. Phil Polstra did with the USB Impersonator, which is basically looks for an authorized device VID/PID and then  impersonates that devices with the VID/PID.

Mitigation

Most probably, you will not need safe mode for the users, so you can just disable it... I mean, it is not that easy, but luckily there is a great blog post on how to do that. BTW, the first page of the post is for Windows XP, but you are not using XP anymore, aren't you? ;)

Alternatively, as I mentioned at the beginning, you might as well use some physical countermeasure (de-soldering/hot-gluing ports). That shit is ugly, but it kinda works.

Conclusion

Next time you will face a device control solution, try out these tricks, maybe they will work, and if they do, well, that's a lot of fun. :)

But don't get me wrong, these device control solutions and similar countermeasures are a good thing and you should use something like this! I know that they make doing business a bit harder as you are not able to plugin whatever USB stick you want, but if you buy a pile of hardware encrypted flash drives, and only allow  those to be plugged in, you are doing it right ;)

Continue reading


  1. Pentest Owasp Top 10
  2. Hacking Images
  3. Pentest Magazine
  4. Hacking Attack
  5. Pentest Red Team
  6. How To Pentest A Website
  7. Hackerrank Sql
  8. Pentest Dns
  9. Hacker Keyboard

Monday, June 8, 2020

Entropy: Netwave And GoAhead IP Webcams Exploiting Tool


About Entropy Toolkit
   Entropy Toolkit is:
  • A set of tools to exploit Netwave and GoAhead IP Webcams.
  • A powerful toolkit for webcams penetration testing.

Entropy Toolkit's installationEntropy Toolkit's execution

Entropy Toolkit's examples:
  • Example of exploiting a single webcam
    entropy -b 1 -i [webcam's ip address and port] -v
    Example: entropy -b 1 -i 192.168.1.100:80 -v
  • Example of exploiting webcams from a list
    entropy -b 2 -l [file text] -v
    Example: entropy -b 2 -l iplist.txt -v
  • Example of exploiting webcams using shodan
    entropy -b 2 -v --shodan [you shodan api key]
    Example: entropy -b 2 -v --shodan PSKINdQe1GyxGgecYz2191H2JoS9qvgD

Entropy Toolkit disclaimer:
   Usage of the Entropy Toolkit for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state, federal, and international laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program.

Entropy Toolkit license: MIT license.

Download Entropy Toolkit
(Sign up Windscribe for free, get full protection and stay anonymous
with the best free VPN. Read more here)
Related posts

  1. Hacking Simulator
  2. Hacker Website
  3. Pentest Book
  4. Pentest Distro
  5. Hacking Gif
  6. Hacker Videos
  7. Pentest Lab Setup
  8. Hackerrank Sql
  9. Pentest Azure
  10. Pentest Free
  11. Pentest Ubuntu
  12. Hacking Youtube
  13. Hacker Ethic
  14. Pentest Ios

How Block Chain Technology Can Help Fight Wuhan Corona Virus Outbreak

As the death toll and the infected cases of widespread coronavirus continue to increase, global organizations and the tech industry has come forward with technology like blockchain to fight coronavirus.

Along with the equipment and monetary support, technology also withstands against the virus with better plans and solutions. Hence, tech industries have started leveraging blockchain technology in the wake of a global health emergency.

Blockchain Helps In Real-Time Online Tracking

The Center for Systems Science and Engineering has already set up an online platform to track coronavirus and visualize the growing number of infected patients in real-time.

But Acoer, an Atlanta-based blockchain app developer, has also launched an alternative online data visualization tool to easily trail and depict the Cororanvirus outbreak using blockchain technology.

Acoer platform, named HashLog, is more advanced and clear as it pulls the data from the Hedera Hashgraph database using the HashLog data visualization engine.

Hedera Hashgraph is an immutable, transparent and decentralized database based on distributed ledger technology that provides synchronized and unchangeable data from the public networks.

Moreover, researchers, scientists, and journalists can use the HashLog dashboard to understand the spread of the virus and act against it swiftly.

For data sources, Johns Hopkins CSSE extracts data from WHO, CDC, ECDC, NHC, and DXY. On the other hand, Acoer maps the public data, including data from the Center for Disease Control (CDC) and the World Health Organization (WHO). Therefore, data may differ on both platforms.
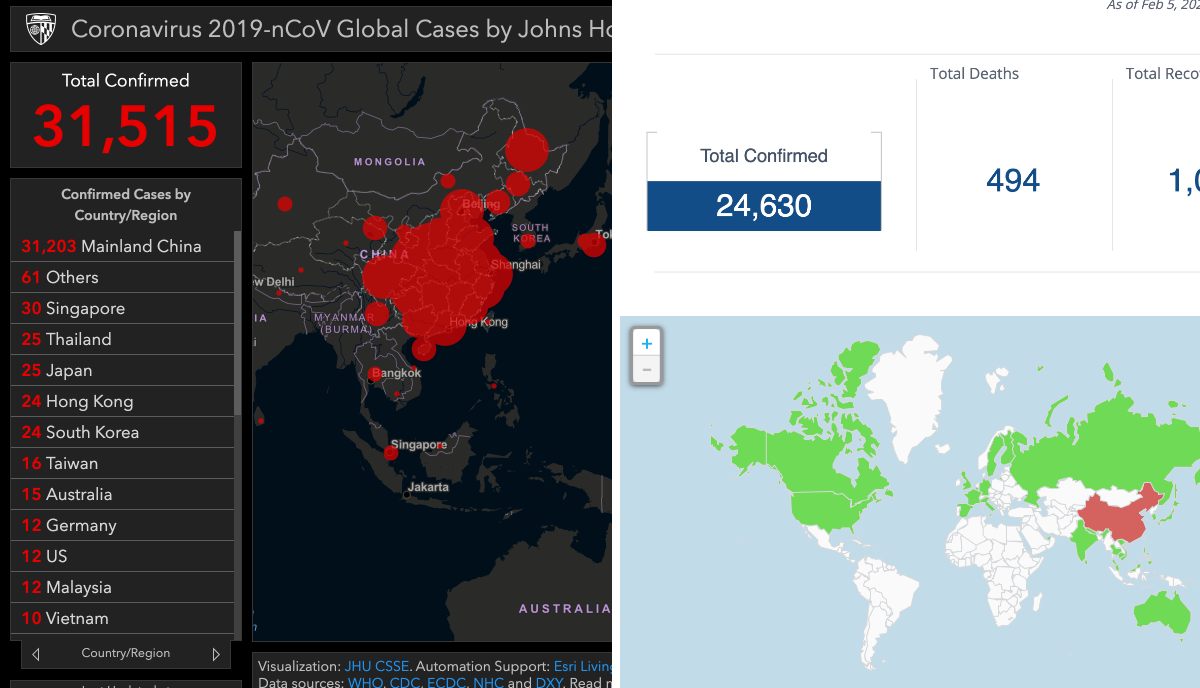
(left) CSSA and Acoer (right)

Blockchain Can Help Monitor And Control Money Flow

To fight the further spread of the coronavirus (2019-nCoV) outbreak globally, China has also received abundant monetary support from the international community to create better action plans.

China's govt-led organization and charities are responsible for overseeing and utilizing the influx of money to research and generate a solution for coronavirus. But due to the lack of coordination and mismanagement among the various organization, money is not being laid out to curb the crisis.

Recently, a paper published by Syren Johnstone, from the University of Hong Kong, discusses the problems encountered by charities, in China and elsewhere. It argues that the present crisis should be seen as a call to arms.

Syren urges for a borderless solution with better management of donations and implementation using the emerging tech like Blockchain and Artificial Intelligence.

Keeping that in mind, Hyperchain, a Chinese company, also announced blockchain-based charity platform to streamline the donation from all over the world.

Since the Hyperchain platform is based on the blockchain, it offers more transparency among the sender and receiver of funds to bring trust and immutability to restrict the transaction data deletion.

Overall, Hyperchain improves administrative function for the money and also extends the logistics actions.

@HACKER NT

Continue reading


  1. Hackintosh
  2. Pentest Tools Github
  3. Pentest Vpn
  4. Hacking With Python
  5. Hacking Forums
  6. Pentest Lab Setup
  7. Pentest Certification
  8. Hacking Link
  9. Pentest Tools
  10. How To Pentest A Website With Kali
  11. Hacking Link
  12. Pentest Ftp
  13. Hacking Bluetooth
  14. Hacking Hardware
  15. Hacker Lab
  16. Pentest Xss
  17. Pentest Practice

BurpSuite Introduction & Installation


What is BurpSuite?
Burp Suite is a Java based Web Penetration Testing framework. It has become an industry standard suite of tools used by information security professionals. Burp Suite helps you identify vulnerabilities and verify attack vectors that are affecting web applications. Because of its popularity and breadth as well as depth of features, we have created this useful page as a collection of Burp Suite knowledge and information.

In its simplest form, Burp Suite can be classified as an Interception Proxy. While browsing their target application, a penetration tester can configure their internet browser to route traffic through the Burp Suite proxy server. Burp Suite then acts as a (sort of) Man In The Middle by capturing and analyzing each request to and from the target web application so that they can be analyzed.


Everyone has their favorite security tools, but when it comes to mobile and web applications I've always found myself looking BurpSuite . It always seems to have everything I need and for folks just getting started with web application testing it can be a challenge putting all of the pieces together. I'm just going to go through the installation to paint a good picture of how to get it up quickly.

BurpSuite is freely available with everything you need to get started and when you're ready to cut the leash, the professional version has some handy tools that can make the whole process a little bit easier. I'll also go through how to install FoxyProxy which makes it much easier to change your proxy setup, but we'll get into that a little later.

Requirements and assumptions:

Mozilla Firefox 3.1 or Later Knowledge of Firefox Add-ons and installation The Java Runtime Environment installed

Download BurpSuite from http://portswigger.net/burp/download.htmland make a note of where you save it.

on for Firefox from   https://addons.mozilla.org/en-US/firefox/addon/foxyproxy-standard/


If this is your first time running the JAR file, it may take a minute or two to load, so be patient and wait.


Video for setup and installation.


You need to install compatible version of java , So that you can run BurpSuite.
Related word
  1. Pentestbox
  2. Hacking Forums
  3. Hackerrank Sql
  4. Pentest Distro
  5. Hacking Tutorials
  6. Pentest Wiki
  7. Pentest Website